Executive Strategic Perspective
Financial institutions and regulatory authorities across the Middle East stand at an unprecedented inflection point. Regulatory frameworks are expanding faster than manual compliance processes can absorb. AML/CFT statutory expectations are intensifying under global FATF evaluations. Cross-border cybersecurity threats continue to target critical financial infrastructure. At the same time, open banking mandates, central bank digital currencies (CBDCs), and rapid fintech innovation are fundamentally reshaping the sector.AICompliREG provides an AI-native, enterprise-grade Governance, Risk, and Compliance (GRC) and Supervisory Technology (SupTech) platform purpose-built for sovereign central banks, monetary authorities, and licensed financial institutions. Unlike conventional multi-tenant cloud GRC platforms, AICompliREG replaces generic off-the-shelf software with Arabic-first legal NLP, strict in-country data sovereignty, and specialized central bank supervisory workflows.
Why RegTech Now? The Regional Supervisory Imperative
Traditional regulatory compliance and supervisory oversight in the GCC rely heavily on disconnected spreadsheets, manual bi-annual returns, disparate audit portals, and labor-intensive document review. When regulations change or emergency circulars are issued, compliance teams scramble to map obligations, while regulators lack real-time visibility into systemic risk concentrations.
AICompliREG transitions state banks and supervised entities from episodic, reactive audits to continuous, automated compliance intelligence:
- Continuous Evidence Collection: Ingests automated telemetry and verifiable evidence from core banking systems, identity networks, and cloud infrastructure, cutting manual compilation by 80%.
- Deterministic Regulatory Mapping: Deconstructs complex legal decrees, circulars, and framework articles into structured, enforceable controls with verifiable parent-child lineages.
- Real-Time Systemic Risk Detection: Correlates prudential risk, anti-money laundering indicators, and cybersecurity incident alerts across institutions to flag contagion before it spreads.
- Audit-Ready Transparency: Generates instant, verifiable audit packages for board oversight, central bank examinations, FATF Mutual Evaluations, and IMF Financial Sector Assessment Programs (FSAP).
The Regional Supervisory Landscape & Operational Gaps
State banks and monetary authorities across the Middle East supervise diverse institutional tiers under multifaceted and rapidly shifting regulatory regimes:
| Regulatory Domain | Regional Legal & Supervisory Instruments | Current Operational Baseline |
|---|---|---|
| Banking Law & Capital | National Banking Laws, Central Bank Decrees, Basel III/IV | Frequent amendments; periodic manual compliance returns |
| AML/CFT Supervision | National AML Laws, FATF Recommendations, FIU Circulars | Bi-annual returns, high false-positive alert burden |
| Cybersecurity Assurance | National Cyber Security Frameworks, Central Bank CS&RF | Incident reporting required within hours; siloed IT evidence |
| Open Banking & APIs | National Open Banking Frameworks, API Specifications | Emerging API ecosystems requiring automated telemetry oversight |
| Fintech Sandboxes | National Sandbox Guidelines, Cohort Directives | Rapid innovation cycles requiring lightweight, agile oversight |
| Digital Onboarding & e-KYC | Central Bank Digital Identity Instructions, UAE Pass, Nafath | Real-time identity verification and biometric audit compliance |
| Data Protection & Sovereignty | National Data Protection Laws, National Cloud Policies | Strict in-country data residency; evolving cross-border rules |
Critical Systemic Bottlenecks Identified
- Fragmented Evidence Silos: AML returns, cyber resilience metrics, capital adequacy calculations, and consumer protection records live in isolated department databases.
- Manual Gap Analysis Friction: Regulators and bank compliance teams spend weeks comparing lengthy policy PDFs against internal operating procedures.
- Delayed Risk Telemetry: Emerging risks in liquidity or cybersecurity are discovered weeks after initial exposure rather than in real time.
- Audit Season Disruption: Preparing for comprehensive evaluations consumes hundreds of high-value officer hours assembling retrospective evidence packages.
- Absence of Unified SupTech Rails: Most international GRC platforms are built for entity-side enterprise compliance and lack central bank supervisory capabilities.
Architectural Transformation: Conventional RegTech vs. AICompliREG
Conventional enterprise GRC and RegTech platforms were originally built for generic corporate IT compliance in Western jurisdictions, focusing on static questionnaires and periodic entity-level self-assessments.
AICompliREG systematically replaces each conventional module with sovereign, Arabic-first, SupTech-native capabilities tailored for Middle East central banking and multi-tier market supervision:
| Conventional RegTech / GRC Module | AICompliREG Sovereign Replacement | Regional Enhancement & SupTech Specialization |
|---|---|---|
| Unified GRC Dashboard | Supervisory Command Center | Real-time compliance heat map covering all licensed banks, fintechs, and payment switches with entity-level drill-down. |
| Governance & Documents | Regulatory Lifecycle Manager | Bilingual (Arabic/English) policy lifecycle: circular drafting → industry consultation → issuance → entity attestation. |
| Committees & Meetings | Governance Hub | Board resolutions, central bank supervisory committee actions, and formal enforcement escalation tracking. |
| Evidence Management | Sovereign Evidence Vault | Central bank return auto-ingestion, high-accuracy Arabic OCR, and tamper-evident blockchain verification. |
| Vendor Risk (TPRM) | Third-Party Oversight | Cloud service provider concentration risk analytics, critical vendor approvals, and cross-border data transfer tracking. |
| Cybersecurity Assurance | Cyber Supervision Center | Automated CS&RF compliance tracking, mandatory 4-hour incident notification workflows, and national CERT threat feeds. |
| Workflow Automation | Supervisory Workflow Engine | Automated enforcement triggers when an entity's risk score exceeds statutory thresholds. |
| Integrations & Identity | SupTech Connector Hub | 50+ pre-built connectors for core banking (Temenos, Finacle), Open Banking APIs, and national digital ID networks. |
| Compliance Assessments | Assessment Engine | 25+ pre-loaded regional regulatory frameworks across prudential, conduct, AML, and cyber domains. |
| Unified Control Library | Unified Control Framework | Article-level statutory mapping where institutions inherit master regulatory controls directly into internal matrices. |
| Enterprise Risk (ERM) | Institutional Risk Register | Dual-horizon risk register: micro-prudential institutional risk alongside macro-prudential systemic stability KRIs. |
| Audit Management | Audit & Evaluation Suite | Instant generation of comprehensive FATF Mutual Evaluation dossiers, IMF FSAP packages, and statutory audit trails. |
| Dashboards & ComplyChat | ComplyChat AR/EN | Sovereign, bi-directional Arabic and English legal NLP capable of answering complex statutory queries from verified decrees. |
| Tiered Deployment | Deployment Spectrum | Multi-tier scaling: Sandbox participants (lightweight), licensed commercial banks (standard), regulator supervision (enterprise). |
Proprietary Modules Unique to AICompliREG
In addition to replacing generic GRC functions, AICompliREG introduces seven sovereign capabilities engineered specifically for central banking and multi-tier market supervision:
01 / Unified Regulatory Reporting (URR)
Extends conventional AML reporting into a consolidated, single-pane regulatory submission portal. Entities submit statutory returns, prudential ratios, and thematic questionnaires through standardized, cryptographically signed API pipelines.02 / Open Banking Supervisory Monitor
Provides central bank regulators with live telemetry on open banking API availability, latency benchmarks, consent revocation rates, and security compliance across all licensed third-party providers (TPPs).03 / FinTech Sandbox Compliance Backbone
Delivers a lightweight, automated compliance container for innovative startups participating in central bank regulatory sandboxes, ensuring regulatory guardrails are monitored without stifling innovation.04 / Arabic Legal & Regulatory NLP Engine
Custom-trained on Middle Eastern legal lexicons, central bank circulars, royal decrees, and sharia governance standards. Automatically extracts obligations, categorizes mandates, and flags conflicts in newly published regulations.05 / GCC Regulatory Interoperability Matrix
Harmonizes cross-border compliance mapping across GCC monetary jurisdictions, facilitating seamless compliance tracking for regional banking groups operating across the UAE, Saudi Arabia, Oman, Qatar, and Bahrain.06 / National Systemic Risk Dashboard
Aggregates anonymized, cross-sectoral risk signals across retail banking, wholesale finance, insurance, and capital markets to provide central bank governors with macro-prudential early warning alerts.07 / Entity Self-Assessment & Attestation Portal
Provides licensed institutions with a secure, self-service environment to benchmark internal controls against newly issued central bank regulations, complete annual attestations, and submit remediation roadmaps.High-Assurance Sovereign Technical Architecture
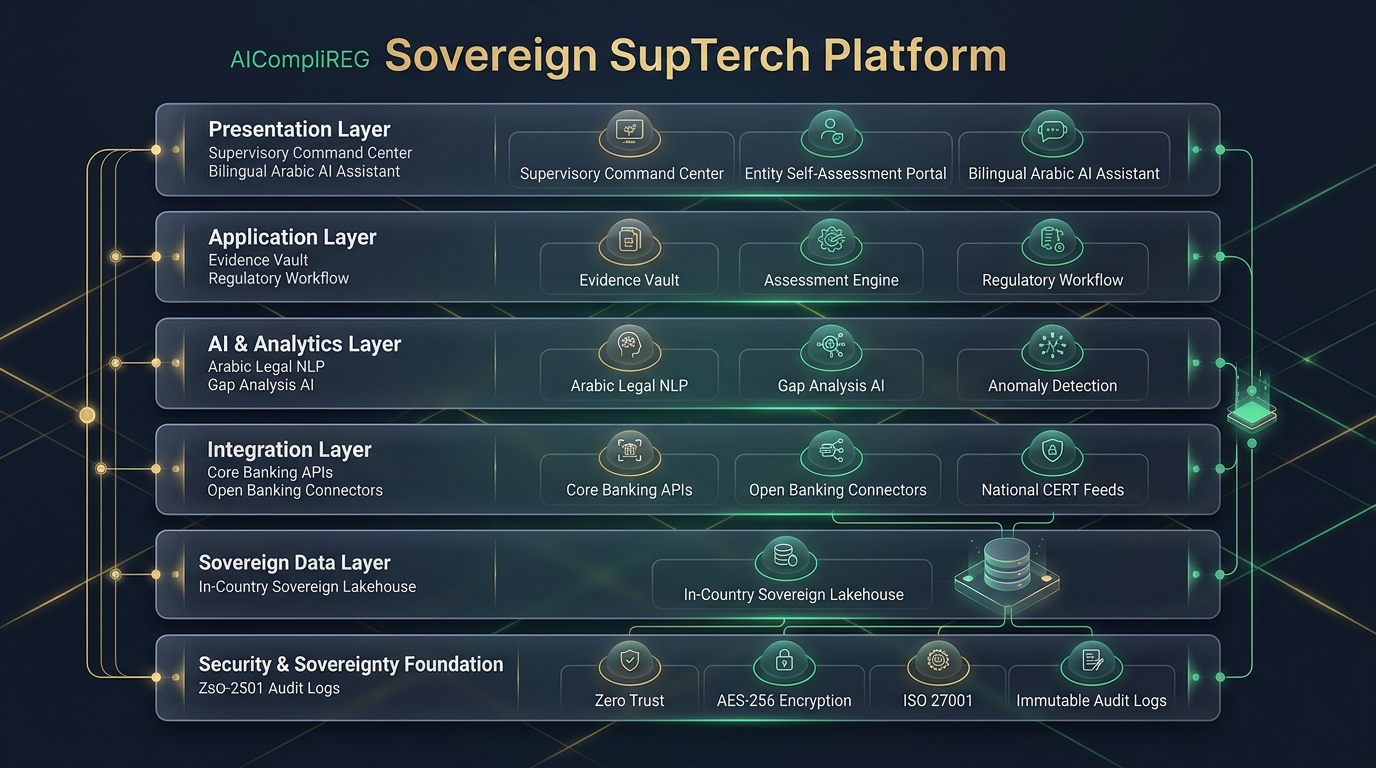
The AICompliREG platform is architected across six defense-in-depth tiers designed to meet the strict sovereignty and resilience standards of GCC central banks:
- Presentation Layer: Bilingual (Arabic RTL & English LTR) interfaces comprising the Supervisory Command Center, Entity Self-Assessment Portal, Board & Executive Briefing Dashboards, and ComplyChat AR/EN.
- Application Layer: Graph-native GRC engines powering the Sovereign Evidence Vault, Article-Level Assessment Engine, Supervisory Workflow Automation, and FATF/IMF Evaluation Suites.
- AI & Analytics Layer: Sovereign, private machine learning runtime incorporating localized Arabic Legal NLP, automated regulatory Gap Analysis AI, Systemic Risk Scoring, and Transaction Anomaly Detection.
- Integration Layer: 50+ pre-built bank-grade connectors for Central Bank reporting APIs, Open Banking frameworks, Core Banking systems (ISO 20022), and National Digital ID fabrics (UAE Pass, Nafath).
- Sovereign Data Layer: Dedicated in-country lakehouse architecture ensuring all regulatory telemetry, evidence tokens, and audit archives remain strictly within national borders.
- Security & Sovereignty Foundation: Enterprise Zero-Trust framework with hardware-backed AES-256 encryption, ISO 27001/27017 controls, and cryptographically verified 7-year immutable audit stores.
25+ Ingested Regional Regulatory Frameworks
AICompliREG comes pre-populated with digitized, article-by-article control mappings for the region’s principal regulatory instruments:
- National Anti-Money Laundering & Counter-Terrorism Financing (AML/CFT) Laws
- National Banking Law & Central Bank Monetary Decrees
- Cyber Security & Resilience Framework (CS&RF)
- National Open Banking Regulatory Framework & Technical Standards
- National FinTech Regulatory Sandbox Guidelines
- National Cloud Computing & In-Country Data Sovereignty Policies
- National Instructions on Digital Onboarding, Biometrics, and e-KYC
- National Payment Systems Law & Retail Payment Service Provider Rules
- Buy-Now-Pay-Later (BNPL) Regulatory & Consumer Protection Frameworks
- Executive Regulations of Regional Capital Market Authorities
- National Personal Data Protection Laws (PDPL)
- FATF 40 Recommendations (Regionally Transposed)
- Basel III / Basel IV Capital Adequacy & Liquidity Standards
- IFRS 9 Financial Instruments Expected Credit Loss Standards
- Corporate Governance Regulations for Banking Institutions
- Central Bank Consumer Protection Principles
- Market Risk Supervision Guidelines
- Operational Risk & Resilience Standards
- Liquidity Risk Management (LCR & NSFR) Directives
- Capital Adequacy & Stress Testing Frameworks
- Related Party Transactions & Exposure Limits
- Fit & Proper Criteria for Significant Function Holders
- Outsourcing & Third-Party Risk Guidelines for Financial Institutions
- Business Continuity Management & Disaster Recovery Standards
- Sharia Governance Frameworks for Islamic Financial Institutions
Phased 12-Month Implementation Roadmap
AICompliREG is deployed through a structured, multi-stage methodology designed to ensure zero disruption to live supervisory operations and immediate time-to-value:
| Phase | Timeline | Core Technical Activities | Milestone Deliverables |
|---|---|---|---|
| Phase 1: Foundation & Sovereignty | Months 1–3 | In-country sovereign cloud or data center staging; Arabic NLP fine-tuning; ingestion of 25+ baseline frameworks. | Sovereign infrastructure operational; baseline regulatory graph digitized; Arabic UI validated. |
| Phase 2: Core Platform & Evidence | Months 3–6 | Sovereign Evidence Vault activation; Assessment Engine rollout; Unified Control Framework mapping; initial reporting API connectors. | Automated evidence ingestion live; AI gap analysis operational; pilot reporting pipelines verified. |
| Phase 3: Supervisory Modules | Months 6–9 | Cyber Supervision Center launch; Third-Party Risk module; Open Banking Monitor; Sandbox Compliance backbone. | Real-time supervisory command center live; entity self-assessment portal deployed to initial cohort. |
| Phase 4: Intelligence & Evaluation | Months 9–11 | ComplyChat AR/EN natural language deployment; National Risk Dashboard aggregation; FATF/IMF audit suite configuration. | Sovereign conversational intelligence active; systemic risk scoring live; audit dossiers auto-generated. |
| Phase 5: Full Cutover & Training | Month 12 | End-to-end user training for central bank examiners and entity officers; parallel run completion; final operational sign-off. | Full enterprise production; multi-entity onboarding underway; continuous supervisory monitoring active. |
Supervised Entity Onboarding Waves
- Wave 1 (Months 8–9): Top 5 domestic systemically important banks (D-SIBs) — deep core integration and supervisory feedback calibration.
- Wave 2 (Months 9–11): Remaining licensed commercial banks, Islamic banks, and digital challenger banks.
- Wave 3 (Months 10–12): FinTech sandbox participants, payment service providers, and digital wallet operators.
- Wave 4 (Month 12+): Insurance underwriters, financing companies, and capital market intermediaries.
Quantified Operational & Strategic Benefits
Implementing AICompliREG delivers measurable efficiency gains across both supervisory authorities and regulated financial institutions:
| Operational Metric | Traditional Manual Baseline | With AICompliREG Platform | Quantified Impact |
|---|---|---|---|
| Evidence Gathering per Entity Cycle | 40–60 officer hours | 8–12 officer hours | 80% reduction |
| Multi-Framework Gap Analysis | 15–20 business days | 2–3 business days | 85% reduction |
| FATF / IMF Audit Dossier Preparation | 6–8 weeks | 1–2 weeks | 75% reduction |
| Cross-Domain Threat & Risk Detection | 48–72 hours latency | Sub-second / Real-time | Continuous surveillance |
| Regulatory Reporting Automation | Manual spreadsheet aggregation | 90% automated | Eliminates transcription error |
| Policy Change Impact Analysis | 10–14 days per circular | Under 2 hours | Instant article mapping |
Security, Data Sovereignty & Zero Trust Architecture
Central bank infrastructure demands the highest security posture in the software industry. AICompliREG is engineered to satisfy sovereign defense-in-depth criteria:
| Security Domain | Operational Controls & Enforcement | Compliance Certification Benchmark |
|---|---|---|
| Data Residency | 100% in-country storage; dedicated sovereign cloud or on-premise government data centers. Zero cross-border data egress. | National Cloud Computing Policy, PDPL |
| Data Encryption | AES-256 encryption at rest; TLS 1.3 encryption in transit with perfect forward secrecy. Hardware Security Module (HSM) key management. | ISO/IEC 27001, FIPS 140-3 Level 3 |
| Identity & Access | Zero Trust Architecture; Mandatory Multi-Factor Authentication (MFA); granular Role-Based Access Control (RBAC) separating regulator and entity scopes. | ISO 27001 A.9, NIST SP 800-207 |
| Application Integrity | Automated SAST/DAST scanning; third-party penetration testing every quarter; continuous vulnerability management. | OWASP ASVS Level 3 |
| Private AI Governance | All LLM and NLP inference executed locally within the sovereign perimeter; zero transmission to third-party consumer AI APIs; complete model auditability. | Ethical AI Frameworks (SAMA / CBUAE) |
| Immutable Audit Logs | Cryptographically signed, append-only audit trail preserving all compliance submissions, assessments, and examiner notes for statutory retention. | FATF 7-Year Record-Keeping Mandate |
Strategic Governance & Institutional Success Metrics
To ensure seamless stakeholder alignment and institutional adoption, AICompliREG implementations operate under a formal three-tier governance model:
- Executive Steering Committee: Chaired by the Central Bank Deputy Governor / Vice Chairman, including Department Heads of Banking Supervision, IT, and Financial Stability.
- Technical Working Group: Composed of central bank regulatory architects, cybersecurity officers, and AICompliREG lead systems engineers.
- Entity Advisory Panel: Selected Chief Compliance Officers (CCOs) and Chief Risk Officers (CROs) from regional commercial and Islamic banks.
Three-Year Multi-Horizon KPI Framework
| Key Performance Indicator | Year 1 Objective | Year 2 Objective | Year 3 Objective |
|---|---|---|---|
| Licensed Entity Adoption | 20 institutions | 50 institutions | 80+ institutions |
| Evidence Automation Rate | 60% of recurring returns | 80% of recurring returns | 90%+ automated |
| Gap Analysis Velocity | 50% cycle time reduction | 75% cycle time reduction | 85% cycle time reduction |
| Continuous Risk Telemetry | 50% of regulatory domains | 80% of regulatory domains | 95% of regulatory domains |
| Regulator Satisfaction Score | 3.5 / 5.0 | 4.0 / 5.0 | 4.8 / 5.0 |
Feature Comparison: Conventional RegTech vs. AICompliREG
| Dimension | Conventional RegTech Platforms | AICompliREG Sovereign SupTech |
|---|---|---|
| Target Sector | Global corporate enterprises | Middle East state banks, regulators & licensed banks |
| Primary Language & Script | English only (LTR) | Native bilingual Arabic (RTL) & English (LTR) |
| Deployment Model | Public multi-tenant cloud SaaS | Sovereign in-country cloud or on-premise air-gapped |
| Regulatory Supervision (SupTech) | Entity compliance only | Full bilateral SupTech (Regulator) + RegTech (Entity) |
| Pre-Loaded Regional Rules | Limited international frameworks | 25+ Middle Eastern frameworks pre-mapped to article level |
| Legal NLP Capabilities | Generic English LLM integration | Custom Arabic legal NLP trained on decrees and circulars |
| Regulatory Reporting Pipelines | None (manual export) | Native bi-directional central bank reporting API connectors |
| Fintech Sandbox Oversight | Not supported | Integrated sandbox compliance and cohort telemetry module |
| Data Residency Assurance | US / EU multi-tenant data centers | 100% in-country sovereign perimeter, zero egress |
Frequently Asked Questions
How does AICompliREG integrate with existing central bank reporting portals?
AICompliREG does not require discarding established investments. Its SupTech Connector Hub provides bi-directional adapters that ingest legacy XML, XBRL, and CSV returns while layering modern automated validation, Arabic OCR verification, and real-time gap analysis on top of historical submission archives.Can regulated entities access the platform without seeing central bank supervisory notes?
Yes. The platform enforces strict cryptographic multi-tenancy with distinct authorization domains. Regulated entities operate inside their private Entity Self-Assessment Portal and can view only their own obligations, evidence submissions, and formal directives. Internal regulator heat maps, supervisor commentary, and cross-institutional systemic risk indicators remain strictly confidential and accessible only to authorized state bank examiners.How does the Arabic Regulatory NLP handle nuanced legal terminology?
The engine is specifically fine-tuned on regional legal corpuses, including GCC ministerial decrees, banking laws, central bank circulars, and Sharia supervisory standards. It recognizes domain-specific phrasing, statutory exceptions, and terminology variations across different GCC jurisdictions with high precision.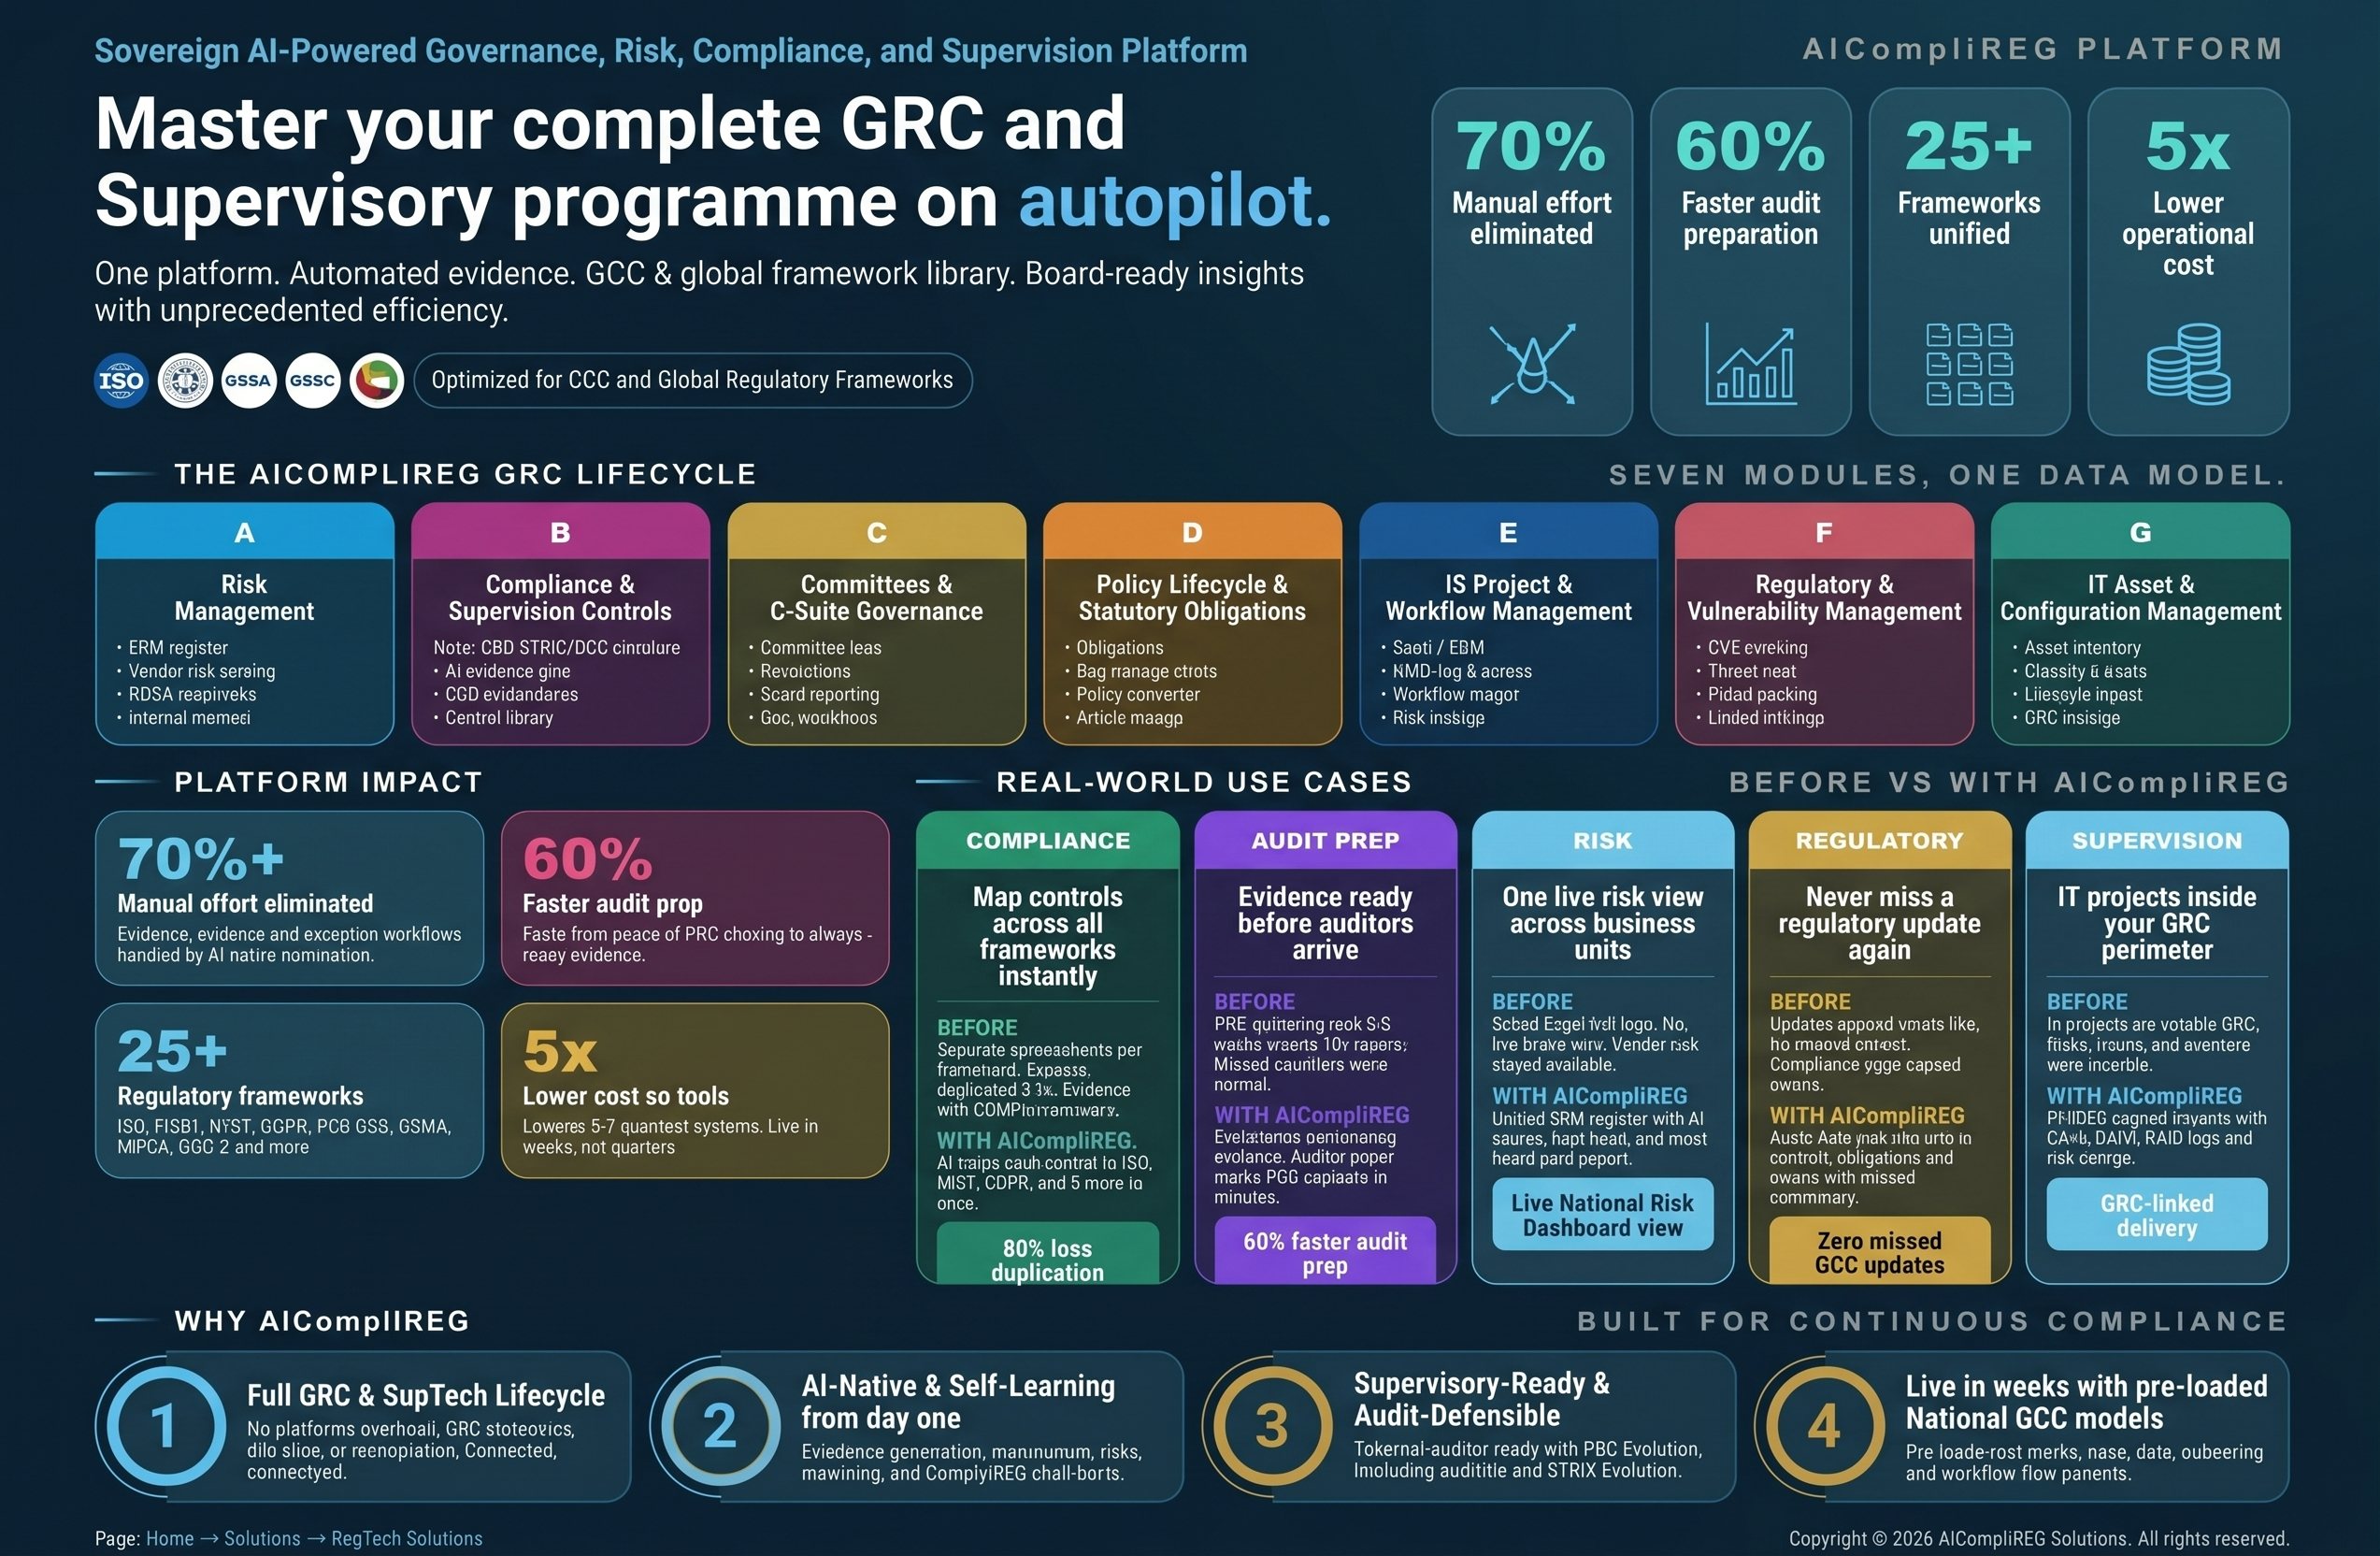
Next Steps & Engagement Model
Fintechify partners with state banks, monetary authorities, and financial institutions to plan, configure, and deploy sovereign RegTech architectures:
- Strategic Discovery & Architecture Workshop (Weeks 1–2): Review current regulatory reporting pipelines, framework priorities, and data residency requirements.
- Framework Mapping & Sovereign Staging (Weeks 3–6): Deploy the sovereign container within your designated perimeter and ingest your prioritized regulatory instruments.
- Pilot Evaluation & Entity Onboarding (Weeks 7–12): Run a guided supervisory assessment cycle with a selected cohort of licensed institutions.
Request a Sovereign Supervisory Demonstration
Ready to modernize regulatory compliance and sovereign financial supervision?
- Request a Demo: Schedule an executive walkthrough with our regulatory technology architects at our DIFC or Muscat offices.
- Consult Our RegTech Specialists: Connect directly with our team to evaluate your statutory framework digitization roadmap.
- Contact Us: Fintechify Assessment Portal
Related Case Studies & Proven Work
Sharjah Islamic Bank (SIB)
Comprehensive digital platform review and benchmarking across four flagship mobile applications, uncovering friction points and delivering an actionable modernization roadmap.
Explore Engagement
Al Rajhi Bank Malaysia · Rize Digital Bank
Next-generation digital bank platform delivering 15-minute personal financing, Ready CashLine credit, digital term deposits, and 99.98% crash-free stability.
Explore Engagement
GCC NeoBank UX Benchmark Report
Comprehensive usability audit evaluating a 34-step onboarding journey, 13 maturity dimensions, wealth marketplace, and conversational AI.
Explore Engagement